TriageForge.
September 2026Whitby · North Yorkshire

TriageForge.

Independent data protection and security engineering.

A practice that does two things most organisations have to hire separately: the data-protection law and the security engineering. Twenty years of UK privacy implementation — DPIAs, ROPAs, breach response — alongside cryptographic design and vulnerability research with fixes shipped in macOS and OpenBSD. Every engagement is scoped in writing and delivered as written work.

Whitby · working remotelyUK GDPR and DUAA 2025Available for engagements
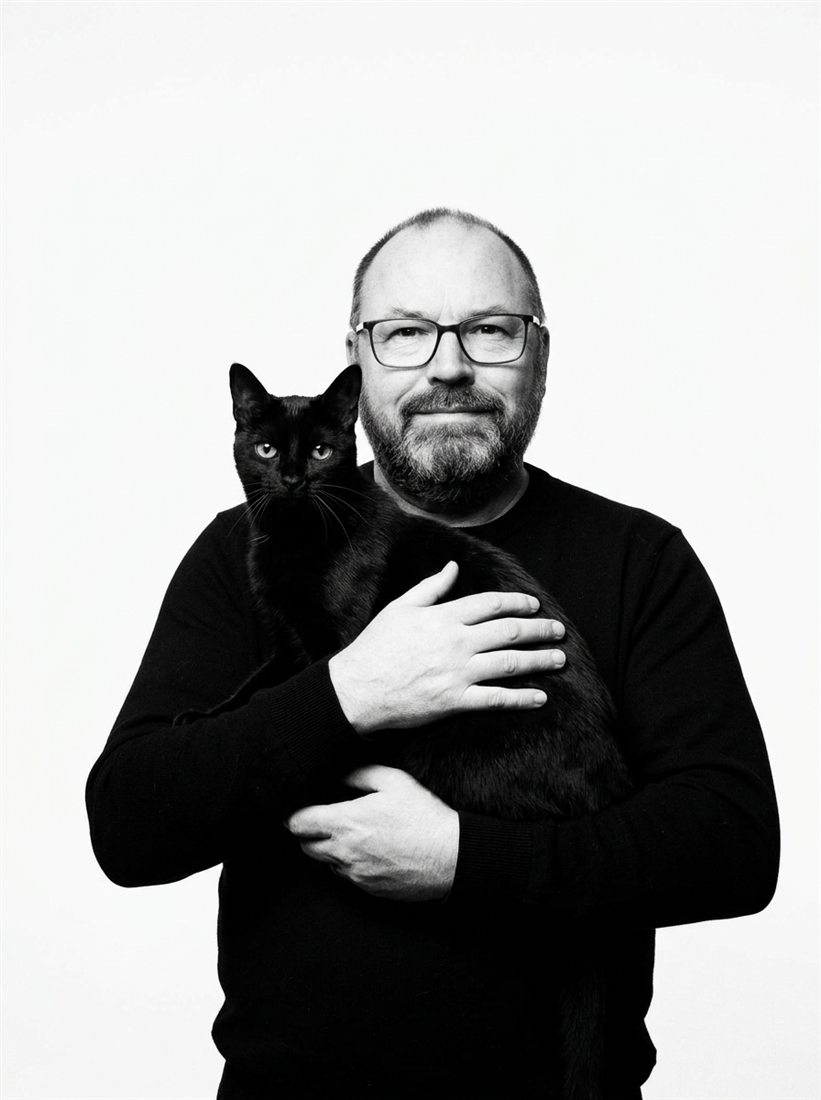
Stuart Paul Thomas holding Abbey, a black cat, against a white studio ground
Plate I · the researcher, with AbbeyAI-rendered to a written brief
01Research

Six areas of focus.

Each area maps to published output: papers, disclosed findings, accepted patches, methodology documents. The work is on the record, which means you can judge it before you commission it.

01

Coordinated vulnerability disclosure

The implicit contract between researcher and vendor. What happens, structurally, when timelines are honoured in form but disengaged in substance.

02

Cryptographic infrastructure

Key management, smart-card and NFC authentication, payment-system architecture. Lineage includes the NHS Approved Cryptographic Algorithms standard (co-author, 2004) and the TfL Oyster contactless design.

03

Kernel-level vulnerability research

Darwin / XNU on macOS; OpenBSD network daemons. Source-level audit paired with binary verification against shipping artefacts. Two CVEs credited by Apple in September 2026.

04

NFC, RFID and physical-token security

EV2First mutual authentication, AES-128-CMAC verification, Secure Dynamic Messaging. The first native open-source NTAG 424 DNA SDK for macOS.

05

Privacy implementation under UK law

UK GDPR, DPA 2018, and the Data (Use and Access) Act 2025. DPIAs, LIAs, ROPAs, transfer impact assessments. Twenty-plus years of implementation experience.

06

Small-lab methodology

How a small practice verifies its claims. Empirical-verification gates between hypothesis and submission. The discipline of declining to file until binary, disassembly and live behaviour agree.

The discipline is the asset; the findings are the receipts.
Approach — principle three
02Publications

Selected publications and disclosures.

Reverse chronological. Entries link to the full public document where one is published.

Apple

Two Apple CVEs — XNU nfsrv_readdirplus and smbd copy-chunk

CVE-2026-84538 · CVE-2026-84553 · shipped 14 September 2026 · macOS Golden Gate 27, Tahoe 26.7, Sequoia 15.8

A missing zero-length guard in the kernel NFS server’s readdirplus path, and unenforced MS-SMB2 copy-chunk limits in smbd. Both addressed with improved input validation. A third report is acknowledged under Terminal in the iOS 27 and macOS Golden Gate 27 advisories.

relayd

RELAYD-001 — OpenBSD relayd CL.TE request smuggling

CWE-444 · latent since 5.2 (2012) · fixed in −current 2026-06-03 · commit e8e5aa2db9c

Thirteen years latent. The body was parsed as chunked but a co-present Content-Length header was not stripped before forwarding, contrary to RFC 9112 §6.1. Found by a targeted source-review pass against the framing rules.

OpenSMTPD

Five OpenSMTPD upstream hardening fixes

Committed 2026-05-26 by Gilles Chehade (poolpOrg@) · credited as diff author

Five commits landed in −current following a corrected per-claim disclosure. The resolution side of the case study at the centre of The Calculator Discipline.

Tooling

Metis — binary vulnerability triage toolchain

Python · angr + Z3 · macOS / Linux / Windows

Path pruning, spectral anomaly, SSA dataflow, symbolic taint, on-device validation — used across the 2026 OpenBSD disclosure batch.

EIGRPD-001

OpenBSD eigrpd — pre-authentication single-packet denial of service

Reported 18 May 2026 · live-validated under ASAN · amd64 only

A worked example of the gap between source undefined behaviour and live exploitability: the stock arm64 build does not crash, owing to the project's stack-protector posture.

Apple

Three macOS disclosures — PING-01, SMB-01A, MAILDROP-01

Apple Security Bounty · published 13 May 2026 · PING-01 and SMB-01A fixed by Apple 14 September 2026

A bounds-check omission, a missing copy-chunk limit, and unsigned client-controlled parameters on icloud.com — the last published 34 months after first report.

Book

macOS Security Research: A Complete Framework

DOI 10.5281/zenodo.19855016 · CC BY-SA 4.0 · free under copyleft

Six-phase methodology distilled from thirty-five years of structured practice. Eleven chapters on disclosure, the Darwin/XNU landscape, and working with vendor security teams.

03Approach

Three principles, applied without exception.

A small research practice depends on being clear about what it knows, what it does not, and how it tells the difference.

Binary first, source second.

The shipping artefact is what runs. Source is intent. Divergence between the two is treated as material until proven otherwise, and the running binary is disassembled before any claim of a live finding.

Evidence over speculation.

Every disclosure carries a working reproducer, a tested version, the vendor reference, and an explicit list of what has and has not been verified. Speculative filings waste vendor time and researcher credibility.

Methodology in public.

The pre-filing adversarial review, the binary-versus-source protocol, and the disclosure-timing calculus are published in full. Critique is welcomed; improvements are integrated.

04People

A single-researcher practice, growing by collaboration.

TriageForge was founded in 2026 by Stuart Paul Thomas in Whitby, North Yorkshire. Thirty-five years of professional practice spanning payment terminals; the Sony PlayStation 2 UK launch network; the NHS Approved Cryptographic Algorithms standard; the Transport for London Oyster contactless payment system; and macOS and OpenBSD vulnerability research published in 2026.

The practice is, at the time of writing, a single-researcher operation. Growth is anticipated through collaboration with researchers in adjacent fields, rather than through employment or capital. The institutional framing — practice, lab, we — describes how the work is structured, not headcount.

Researchers active in cryptographic infrastructure, coordinated disclosure, kernel-level research, NFC and smart-card security, privacy implementation, or small-lab methodology are invited to make contact regarding specific collaborations. Co-authorship and credited contributions follow standard academic practice.
05Engagements

What the practice is engaged to do.

Two disciplines that normally have to be bought separately: the law that governs personal data, and the engineering that actually protects it.

01

Data protection officer, fractional

The named or supporting DPO role for organisations that need it without the headcount. DPIAs, LIAs, ROPAs, vendor schedules, retention, breach response, staff training.

02

Privacy programme work

UK GDPR, the Data Protection Act 2018 and the Data (Use and Access) Act 2025. Gap assessments, transfer impact assessments, subject-access handling, and policy that survives contact with a regulator.

03

Cryptographic and design review

Key management, smart-card and NFC authentication, payment-system architecture. The discipline behind the TfL contactless key design and the NHS algorithms standard, applied at the scale you actually have.

04

Vulnerability assessment

Source-level audit paired with binary verification against the artefact you ship. Findings arrive with a working reproducer and an explicit list of what has and has not been verified.

05

Disclosure support

Running coordinated disclosure with a vendor, or receiving it well. Triage, evidence discipline, timeline management, and the judgement to decline to file when the evidence does not hold.

06

Written technical opinion

Analysis for legal, regulatory or insurance contexts, written to be read by people who will test it. Plain English, with the reasoning and the uncertainty both on the page.

Engagements run in writing. Scope, deliverable and timescale are agreed by email before anything starts, and the result arrives as a document you can hand to an auditor, a regulator or an engineer — not a meeting you have to take notes in. Rates depend on scope and are quoted up front.

Community groups, charities and small research teams: a limited amount of pro bono work continues alongside the paid work. Say so in your first email.

06Contact

Enquiries by written email.

Written enquiries welcome. Outline the problem, the timescale you are working to, and any constraint you already know about.

contact@triageforge.co.uk

TriageForge takes paid engagements in data protection and security, and a limited amount of pro bono work for community, charity and research organisations. It does not take retainers, investment, or work that depends on a conflict of interest being overlooked.

General

contact@triageforge.co.uk

Privacy Research Requests

privacy@triageforge.co.uk

Vulnerability reports

security@triageforge.co.uk